
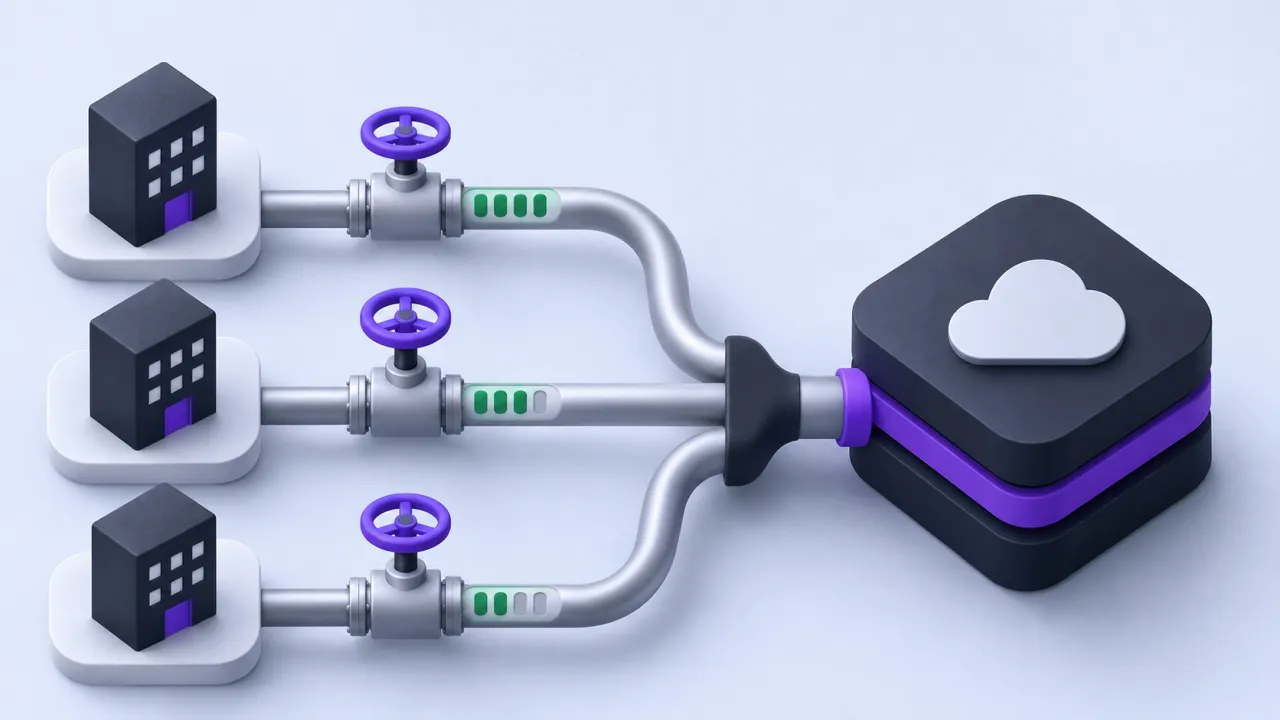
Rate limiting should protect shared capacity without allowing one noisy tenant to dominate every other customer. A single global limit may defend infrastructure while producing unfair outcomes. Define the unit being limited, the customer boundary and the response clients should follow when their budget is exhausted.
The contract to define first
Consider separate limits for expensive operations, bursts and sustained use. Derive tenant identity from authenticated context rather than a caller-controlled header. Make retry responses useful and avoid leaking another tenant’s consumption. Internal jobs and administrative operations need explicit policies rather than accidental exemptions.
A worked scenario
A synthetic tenant starts a bulk import while another performs ordinary reads. An operation-aware budget can keep the import bounded without blocking unrelated interactive traffic. The test should measure the second tenant’s experience as well as the first tenant’s limit enforcement.
An implementation and review sequence
- Define tenant identity and operation cost classes
- Specify burst sustained and shared-capacity policies
- Test fairness under concurrent workloads
Failure cases worth testing
| Condition or input | Expected behavior |
|---|---|
| Caller changes a tenant header | Authenticated identity still defines the budget |
| One tenant starts a bulk task | Other tenants retain the planned service level |
| A limit is reached | The client receives a documented retry response |
Download the illustrative acceptance checklist (JSON)
Tradeoffs and limits
Distributed counters add consistency and availability tradeoffs. A simpler per-instance mechanism may be adequate for a narrow product, but it should not be described as a strict global guarantee.
Use the result to make a decision
The practical output is straightforward: compare fairness burst budgets and retry responses. Keep the assumptions with the artifact so a product owner, implementer or prospective partner can review the same decision. A useful handoff states the supported scope, the evidence collected and the remaining dependency instead of treating a successful demonstration as proof of every operating condition.
Continue with related implementation detail
Related guide: Multi-tenant SaaS data isolation with FastAPI and PostgreSQL
SaaS deletion propagation architecture
References and current platform requirements
Google Cloud: Cloud Run documentation
Firebase: test Firestore security rules
The linked references provide platform or process context. The worked scenario and acceptance matrix are original examples; adapt them to the actual product, supported environment and documented responsibilities.
Discuss the workflow
Discuss one reliability bottleneck, its impact, and a measurable acceptance task.
Explore the relevant AptixLabs service
What makes tenant rate limiting fair?
Rate limiting should protect shared capacity without allowing one noisy tenant to dominate every other customer. Distributed counters add consistency and availability tradeoffs.
Which failure cases should be included in the review?
Include these explicit cases: Caller changes a tenant header: authenticated identity still defines the budget; One tenant starts a bulk task: other tenants retain the planned service level; A limit is reached: the client receives a documented retry response.